Improve your WordPress SEO: Write better content and have a fully optimized WordPress site using the Yoast SEO…
About DoLogin Security
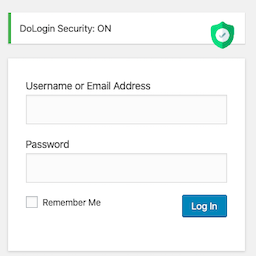
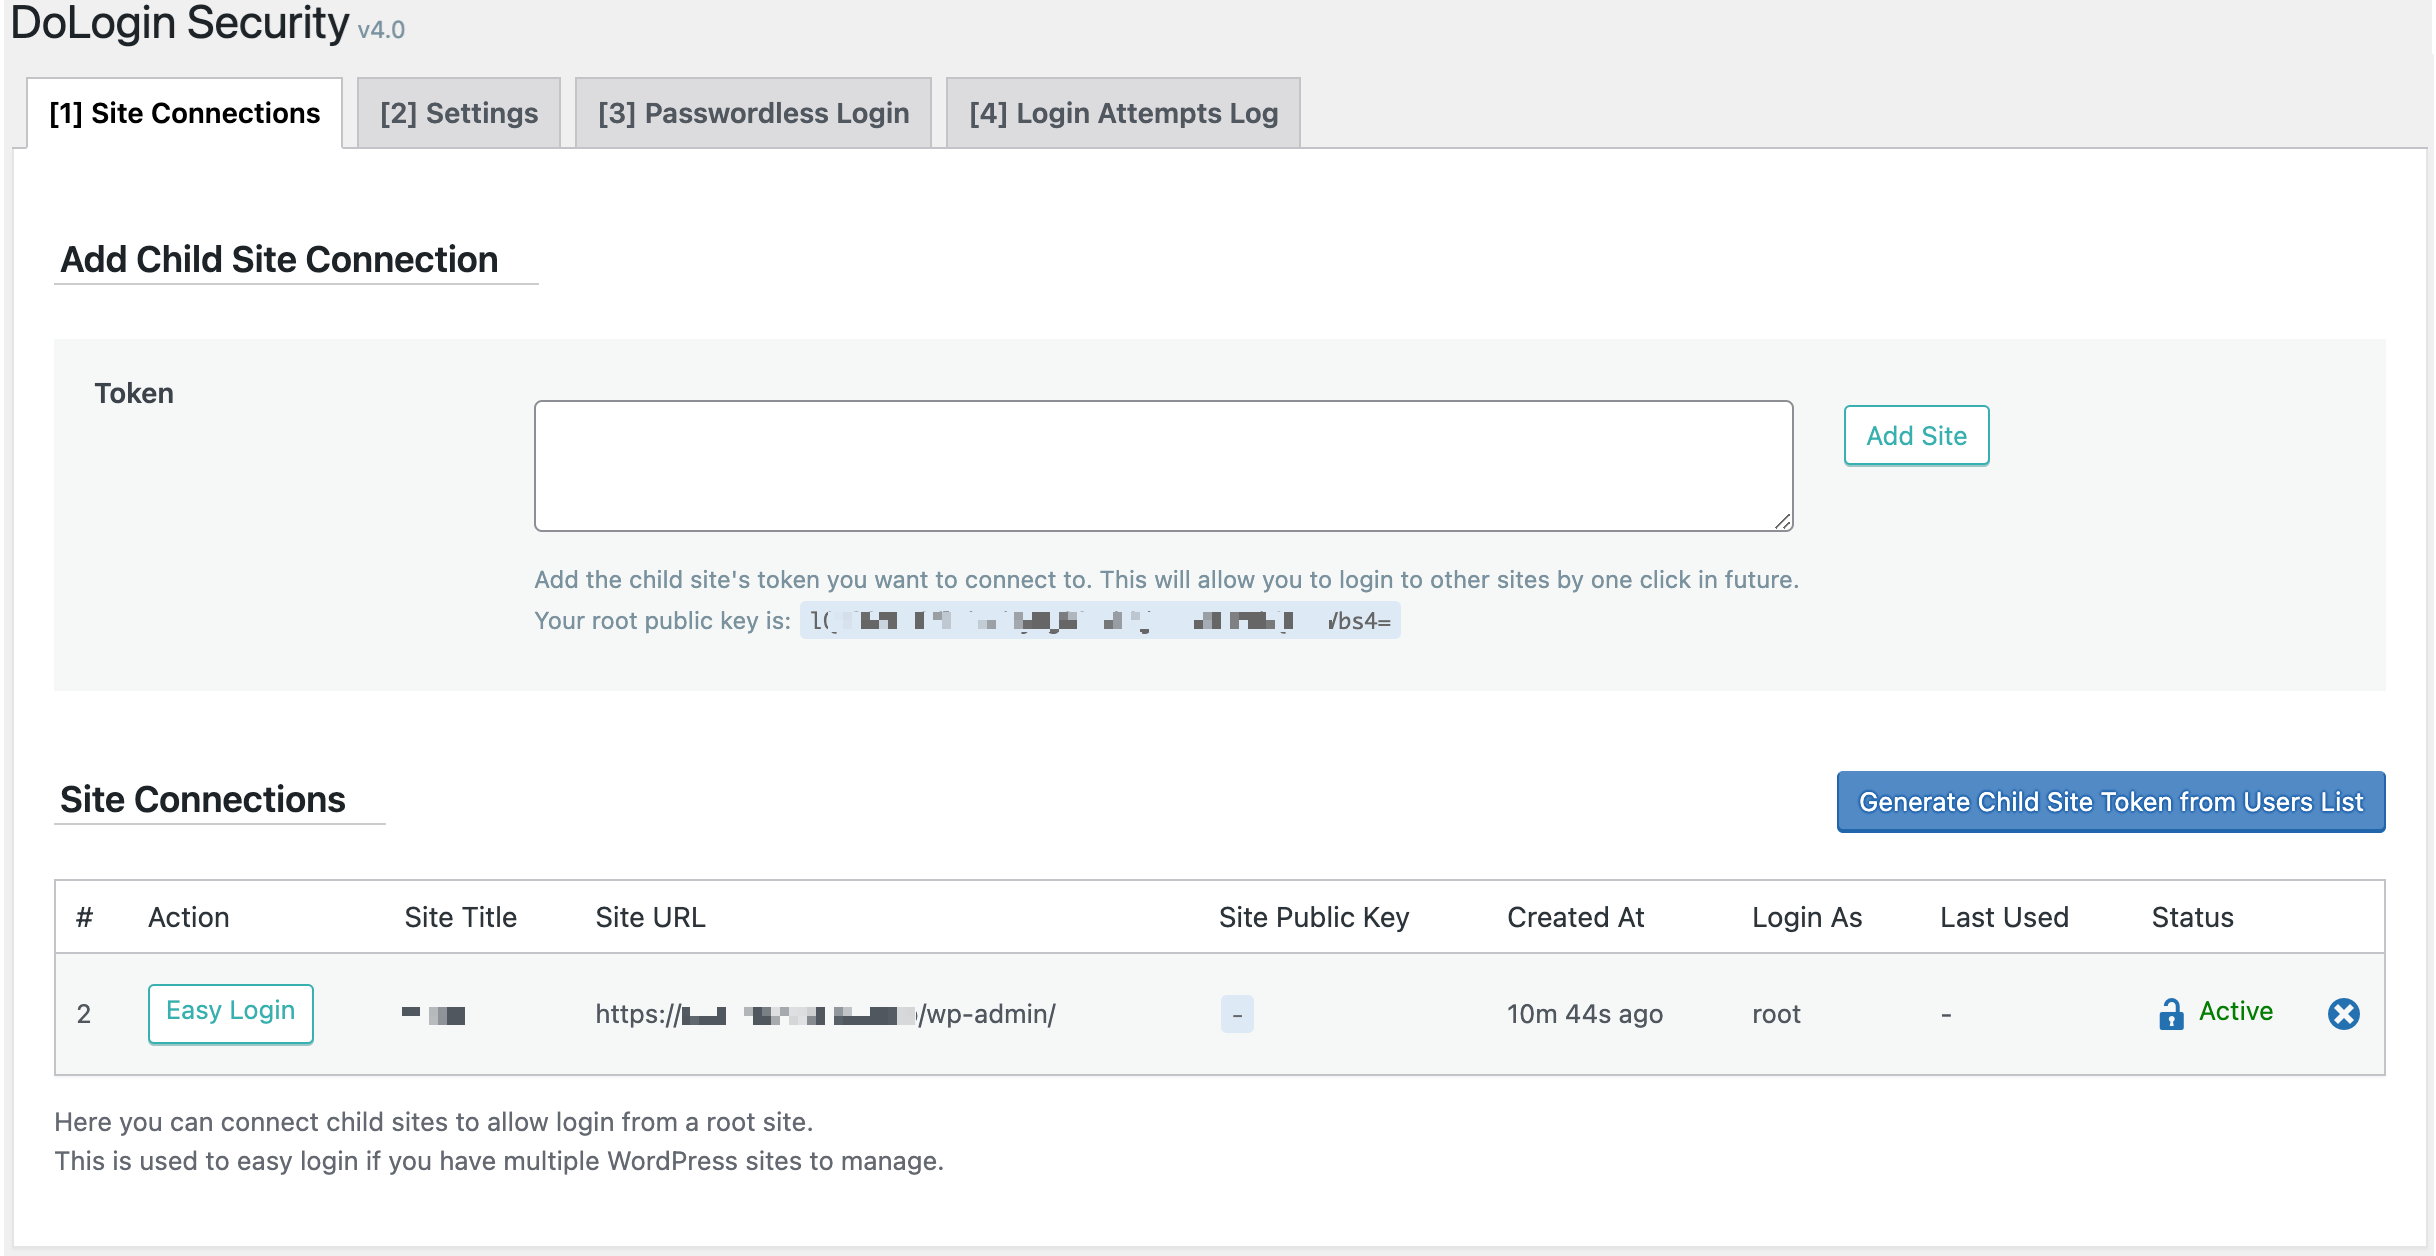
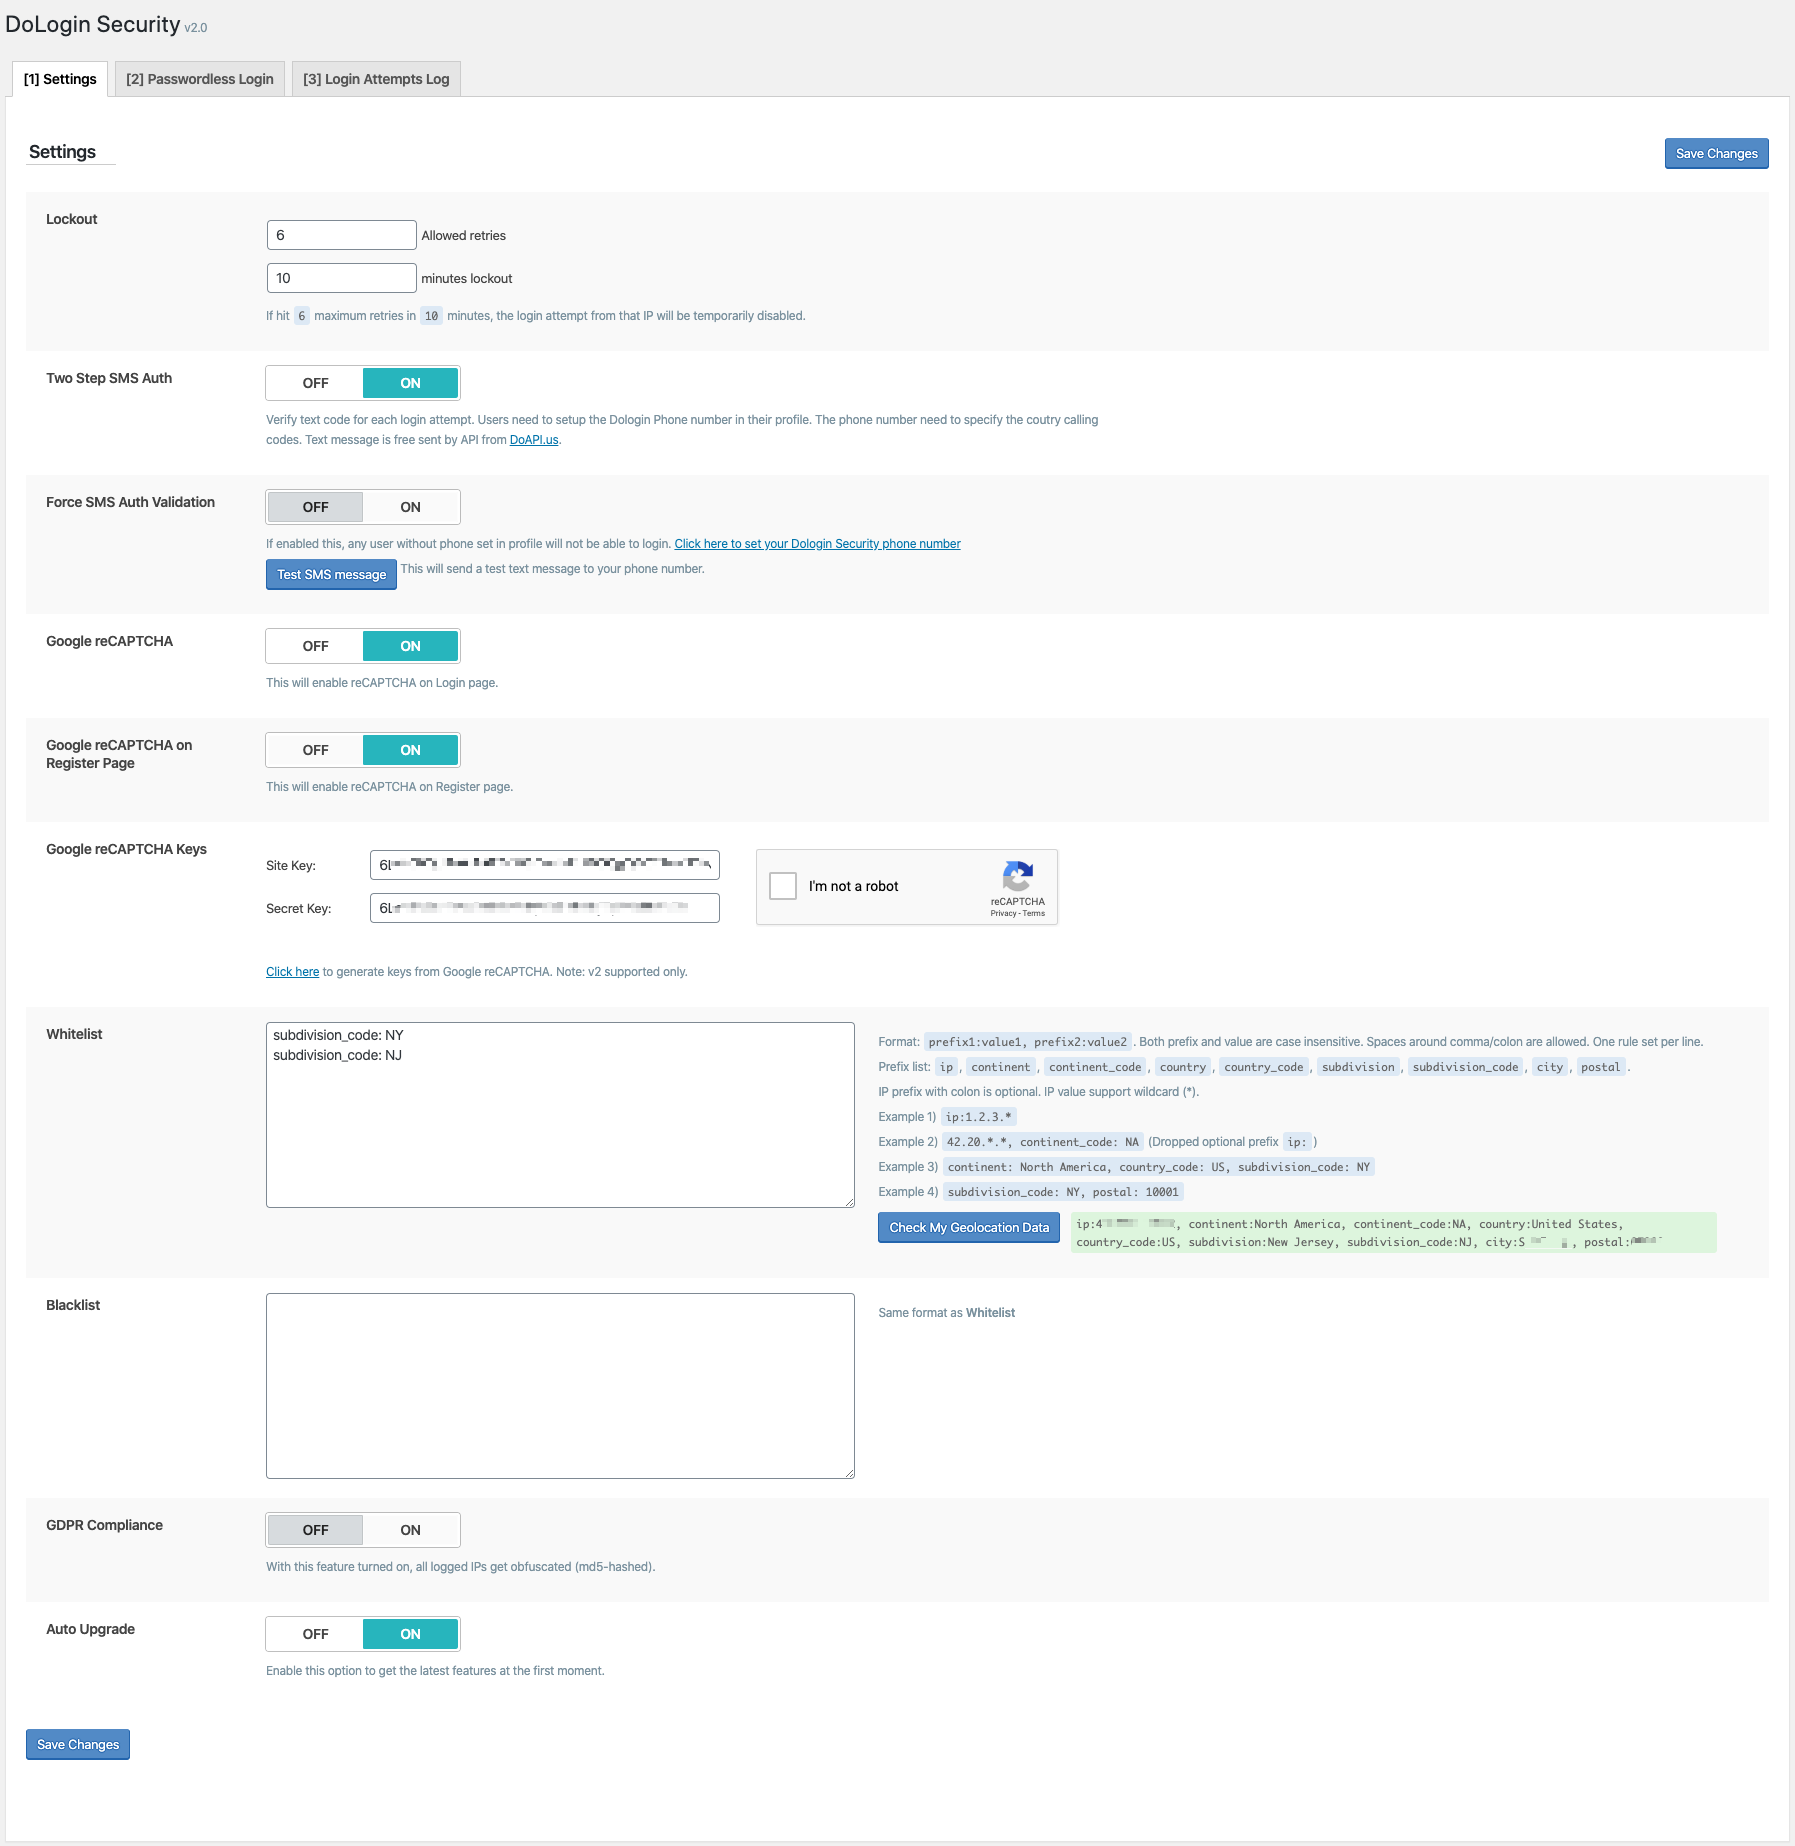
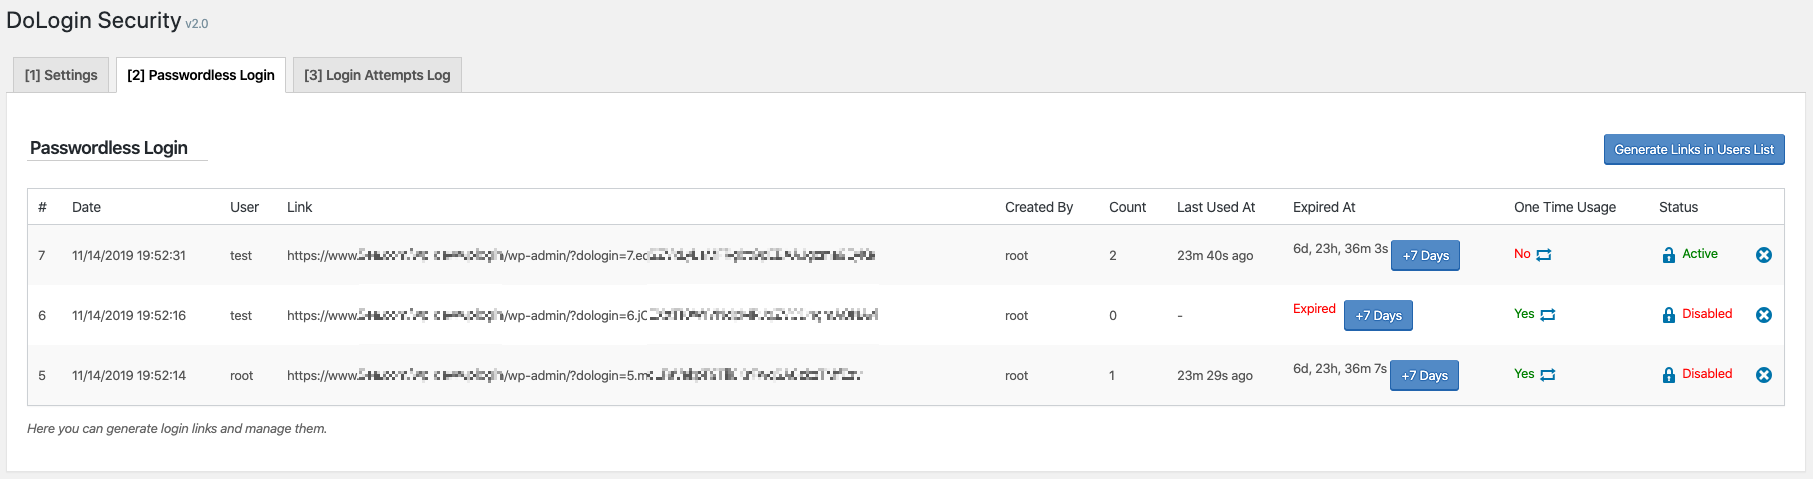
This plugin provides smart brute force attack protection for your WordPress login page. It limits the number of login attempts and offers features such as two-factor authentication, text SMS message passcode, Google reCAPTCHA, and GeoLocation/IP range restrictions. It is also GDPR compliant and supports WooCommerce login.Screenshots
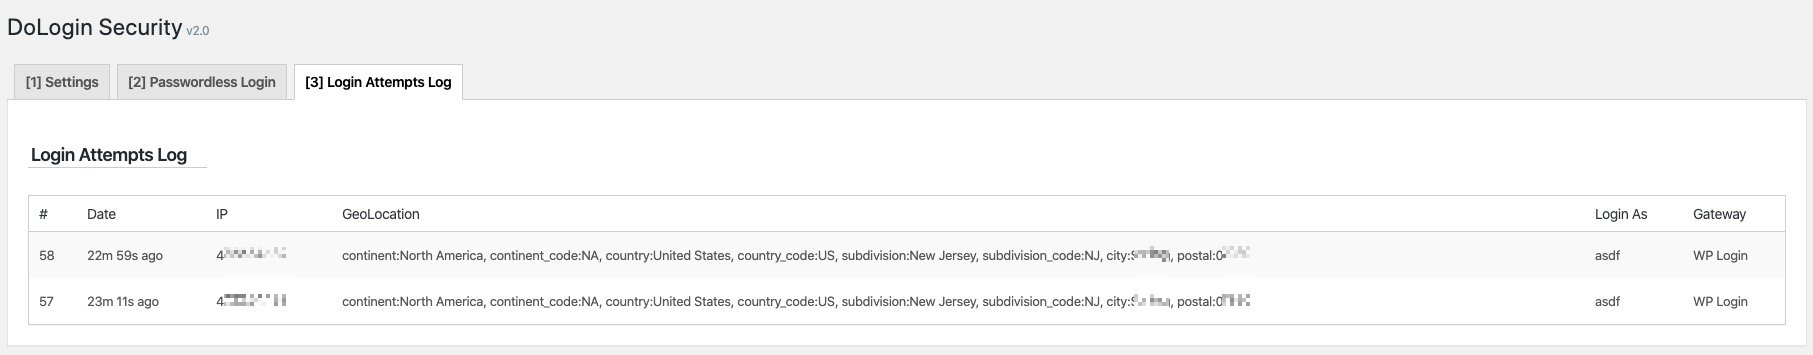
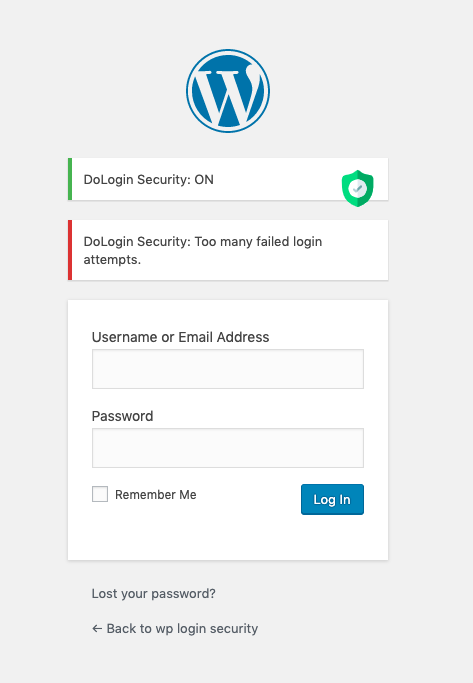
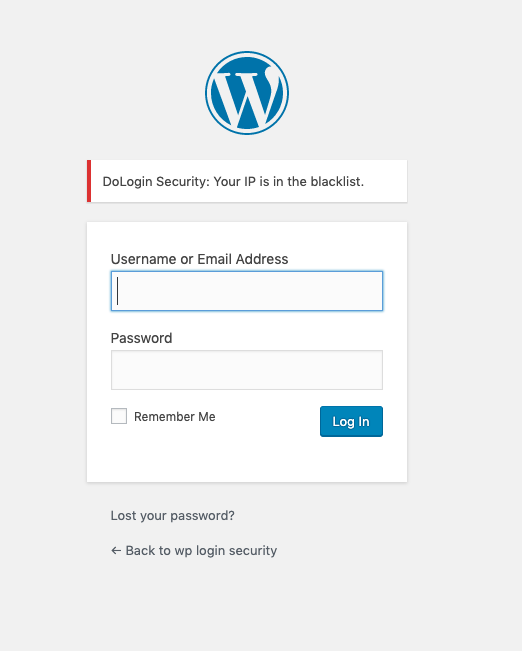
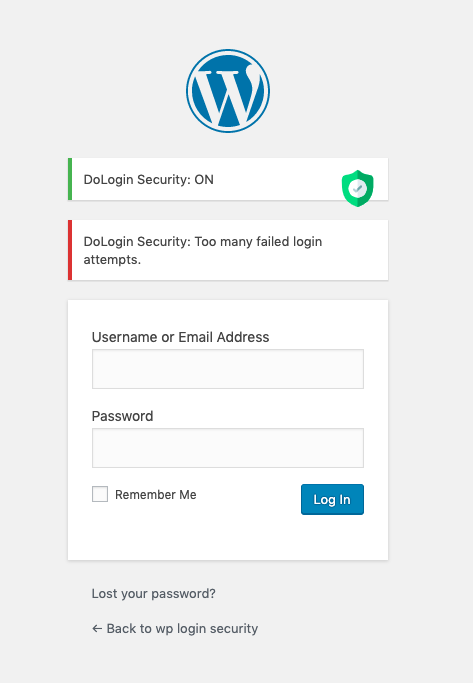
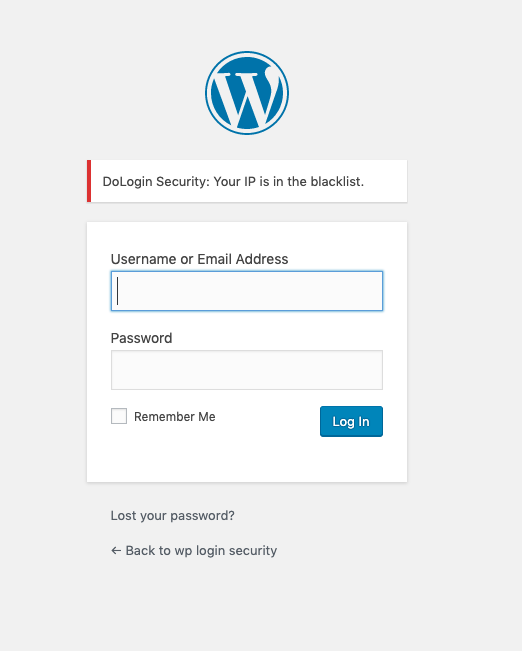

Changelog
3.8
- Security patch per patchstack report.
3.7.1
- IP vulnerability patch for dashboard widget. (Bob@Jetpack)
3.7
- IP vulnerability patch. (Bob@Jetpack)
3.6
- Fixed Google reCAPTCHA authentication failure. (mandotr)
3.5.2
- Fixed auto upgrade PHP warning. (lavacano)
3.5.1
- Banner to install qrcode plugin to enable 2FA.
3.5
- ? Two-factor Authentication.
3.4
- Bypassed version check to speed up WP6 loading.
3.3
- Fixed potential duration value in string conversion issue. (wpcrono)
3.2
- API
dologin_admin_menu_accessto allow other users to config dologin settings. (franfal)
3.1
- Compatibility improvement when communication failed between client wordpress and DoAPI.us API. (@matteocuellar @ecomturbo @thesaintindiano)
3.0
- ? Dashboard widget.
- New API for free text message gateway.
2.9.4
- Fixed IXR_Error PHP notice for XMLRPC login failure.
2.9.3
- Support translation for login text message. (@merkwert)
2.9.2
- More accurate to detect IP.
2.9.1
- ? New setting Google reCAPTCHA on Lost Password Page.
2.9
- WordPress v5.5 Rest compatibility.
2.8
- Avoid duplicated login attempt records for one IP in a short time.
- GUI enhancement.
2.7.1
- Added API info to GUI.
2.7
- Login Attempts log can be cleared now.
2.6
- Codebase reformated.
2.5
- CLI supported.
2.4
- Passwordless link can be copied in one click.
2.3
- ? Reverse Matching w/
!:feature. Now can use!:to exclude one rule. (@jacklinkers)
2.2.2
- Better IP detection.
- Supported empty line and single line comments for whitelist and blacklist.
2.2.1
- Declared WooCommerce support up to 4.0.1.
2.2
- Whitelist and Blacklist support comments now.
2.1
- Passwordless login will now have a confirm page to avoid auto-visited when sharing the link.
2.0
- Fresh New GUI!
1.9
- ? New option: Show reCAPTCHA on Register page. (@ach1992)
1.8
- ? Show Phone Number field on Register page if Force SMS Auth setting is ON. (@ach1992)
1.7.1
- ? Will now honor the timezone setting when showing date of sent. (@ducpl)
1.7
- Supported DoDebug now.
- Bypassed whitelist check for WooCommerce clients on checkout page.
- ? WooCommerce checkout page can now login correctly.
1.6
- ? Google reCAPTCHA.
- ? WooCommerce can now use same login strategy settings.
1.5
- ? Test SMS Message feature under Settings page.
1.4.7
- Language supported.
1.4.5
- PHP5.3 supported.
1.4.4
- Doc updates.
1.4.3
- API Silent install mode to avoid redirecting to settings by defining const
SILENCE_INSTALL
1.4.2
- API Generated link defaults to expire in 7 days.
1.4.1
- API New function
dologin_gen_link( 'my_plugin' )API to generate a link for current user.
1.4
- ? Passwordless login link.
1.3.5
- SMS PHP Warning fix.
1.3.4
- REST warning fix.
1.3.3
- GUI cosmetic.
1.3.2
- ? Fixed a bug that caused not enabled SMS WP failed to login.
1.3.1
- PHP Notice fix.
1.3
- ? SMS login support.
1.2.2
- Auto redirect to setting page after activation.
1.2.1
- Doc improvement.
1.2
- ? XMLRPC protection.
1.1.1
- ? Auto upgrade can now check latest version correctly.
1.1
- ? New Display login failure log.
- ? New GDPR compliance.
- ? New Auto upgrade.
- GUI Setting link shortcut from plugin page.
- GUI Display security status on login page.
- ? Stale settings shown after successfully saved.
- ? Duration setting can now be saved correctly.
- ? Fully saved geo location failure log.
1.0 – Sep 27 2019
- Initial Release.