The Elementor Website Builder has it all: drag and drop page builder, pixel perfect design, mobile responsive editing,…
About Disable XML-RPC-API
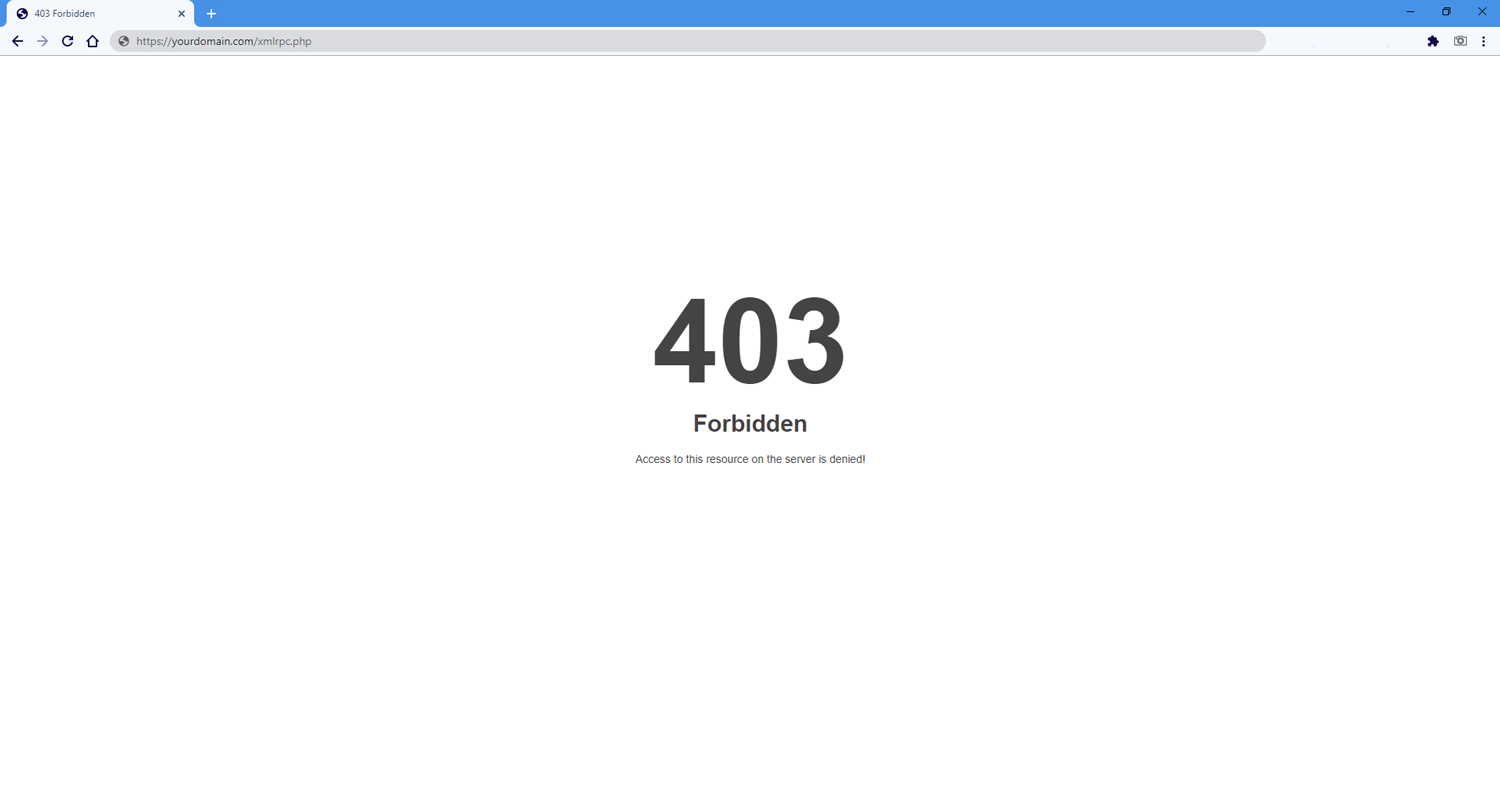
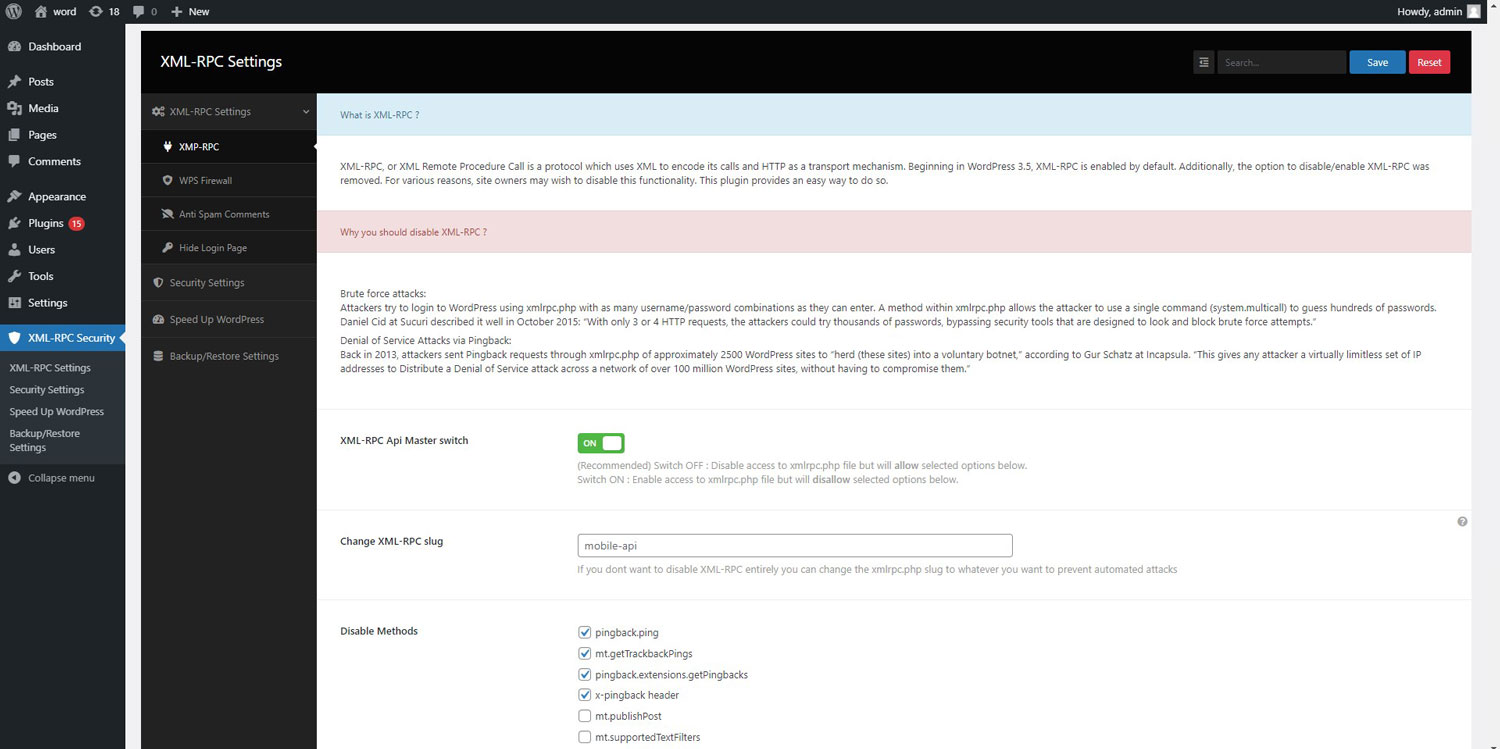
This plugin protects your WordPress website from xmlrpc brute-force attacks, DOS and DDOS attacks by disabling the XML-RPC and trackbacks-pingbacks. It also has additional features such as disabling access to xmlrpc.php file, changing htaccess file permission, disabling X-pingback, and more. Disabling XML-RPC is important as it prevents brute force attacks and denial of service attacks via pingback.Screenshots
Frequently asked questions
What is XML-RPC?
XML-RPC, or XML Remote Procedure Call, is a protocol that uses XML to encode its calls and HTTP as a transport mechanism. It has been enabled by default in WordPress since version 3.5, and the option to disable or enable it was removed. This plugin provides an easy way to disable this functionality.
Why should I disable XML-RPC?
XML-RPC has two main weaknesses: brute force attacks and Denial of Service (DoS) attacks via Pingback. Attackers can use xmlrpc.php to try many username/password combinations with a single command, bypassing security tools. Pingback functionality can also be exploited for DoS attacks.
What are some key features of this plugin?
This plugin allows you to disable access to the xmlrpc.php file, automatically change the .htaccess file permission to read-only, disable X-pingback to minimize CPU usage, and remove the pingback-ping link from the header. It also offers options to disable selected methods from XML-RPC, rename the XML-RPC slug, and blacklist or whitelist IPs for XML-RPC. Additionally, it can disable the JSON REST API, hide the WordPress Version, and disable the built-in WordPress file editor.
Changelog
1.0.0
- Initial release
1.0.1
- Fix bugs
1.0.5
- Remove pingback link tag in header
- Add ability to fix htaccess file permission
1.0.6
- Fix warnings for htaccess permission
1.0.7
- Fix blank page when using W3 Total Cache and some other cache plugins
1.0.8
- Fix code conflict with Autoptimize plugin
1.0.9
- WordPress 5.7 compatible
- Fix some issues
2.0.0
- Fix code conflict with some other plugin
- Fix hiding data in WooCommerce Product Tabs
2.1.0
*Major Update
*Add “XML-RPC Security”settings menu
*Add some new features
*Fix plugin deactivation bug
2.1.1
- Add new feature fix hotlinks
- Change notif timing
2.1.2
- Add an option to disable auto change htaccess permission
- Fix “DISALLOW_FILE_EDIT” warning
- WordPress 5.8 compatibility
2.1.3
- Fix compatibility issue with WordPress 5.9
- Fix htaccess cleaning function
2.1.4
- Fix some minor bugs
- Refactor the entire codes
- Add a fallback function for situations htaccess is not working
2.1.4.2
- Hotfix for error on update
2.1.4.3
- Hotfix for error on removing v metadata
2.1.4.4
- Fix warning undefined variable $htaccess_code when disable hotlink fix is off
- Fix warning Undefined array key “plugins” on PHP 8+
2.1.4.5
- Fix removing vpingback header issue in the last major update
- Update tested up to wp 6.1
2.1.4.7
- Fix issues on vuninstallation hook
- Minor improvements on admin review notification
2.1.4.8
- Fix bug v wp reset API option
2.1.4.9
- Update Jetpack default whitelist IPs
- Fix bug with update actions function
- Keep enabling WP RSS in default settings
- Test with WordPress 6.3 and update tested up to
2.1.5
- Hotfix for .htaccess error and disabling the admin notices
2.1.6
- Clean Up the plugin codes (remove unnecessary codes)
- Add VaultPress IPs to JetPack allowlist
- Test compatibility with WordPress 6.6.1
2.1.7
- Improve disable xmlrpc fallback method
- Test compatibility with WordPress 6.7.1

